Every web page reaches you through HTTP. Add the S and it travels sealed, so nobody along the way can read it or change it.
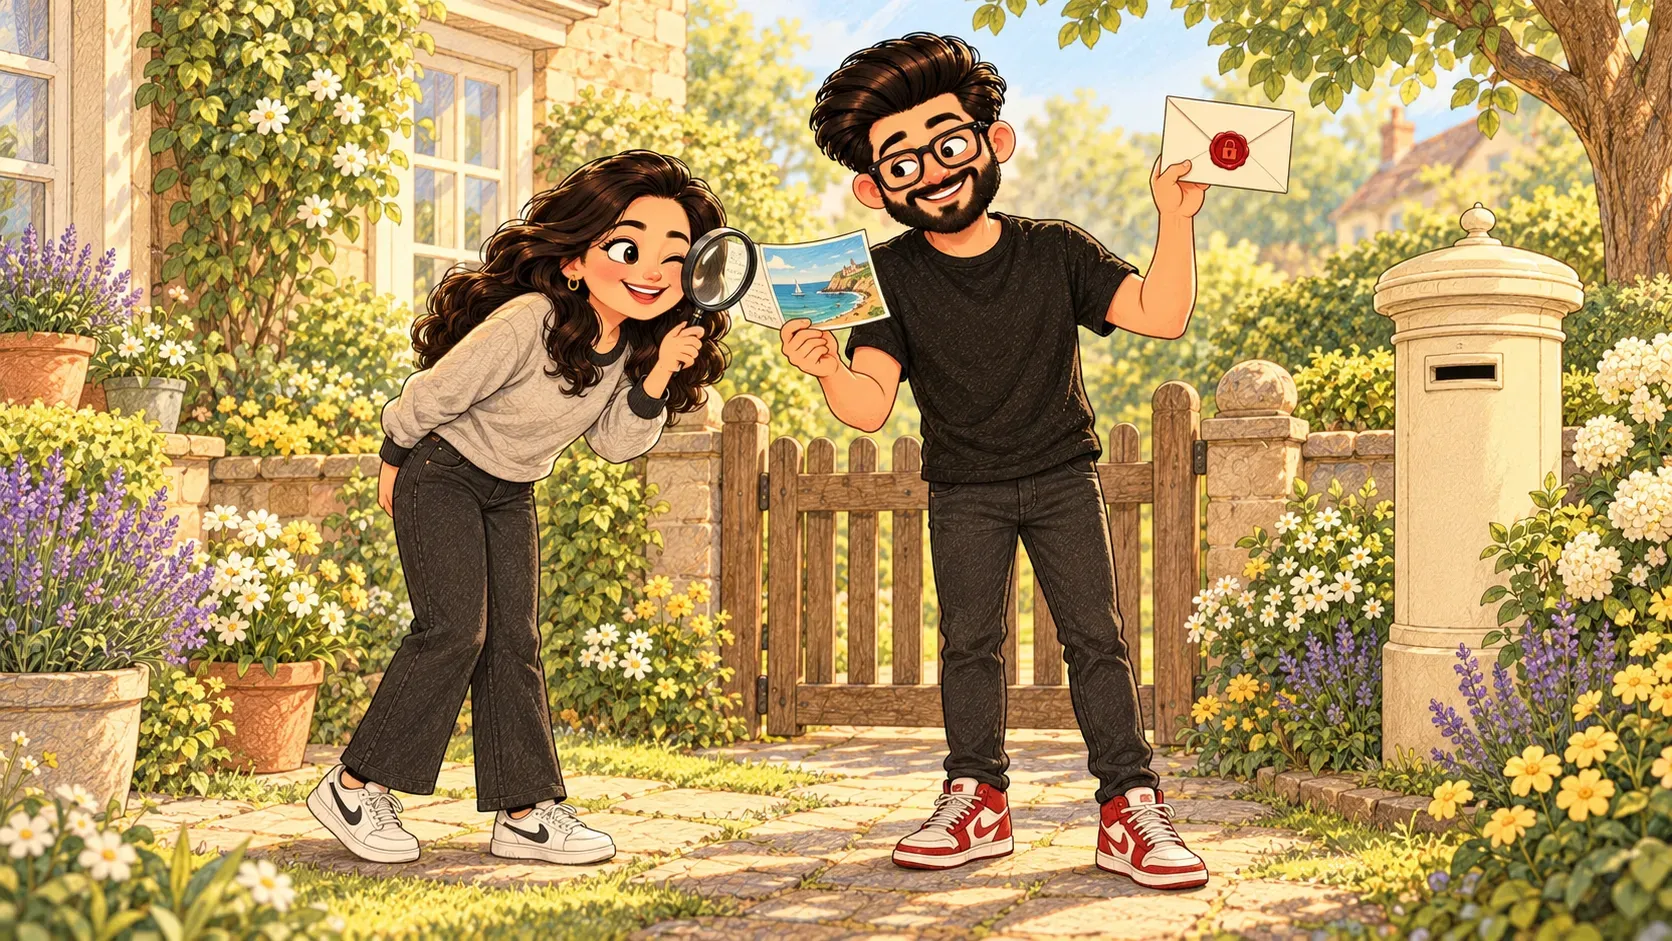
A postcard is quick and easy. But everyone who handles it along the way can read it: the postman, the sorting office, anyone who picks it up. A sealed envelope carries the same message, yet only the person it’s addressed to can open it.
HTTP is how your browser asks a website for a page and how the website sends it back. On its own, it’s a postcard. HTTPS is the same conversation sealed in an envelope that only your browser and the website can open.
How you can tell
Secure websites start with https:// and usually show a small padlock or settings icon next to the address. Plain HTTP websites get a “Not secure” warning.
Why it matters
Your data hops through many machines on its way: your Wi-Fi, your internet provider, networks in between. Over plain HTTP, any of them could read your password or quietly change the page. HTTPS scrambles everything, so they only see gibberish. It also proves you’re talking to the website that really owns that address, not an impostor.
Today almost every website uses HTTPS. Browsers warn you when one doesn’t.
What it isn’t
It doesn’t make a website trustworthy. A scam website can have a padlock too. HTTPS protects the journey, not what’s waiting at the other end.
Where the comparison breaks down
Even with a sealed envelope, the postman can still see who it’s addressed to. HTTPS is similar. People along the way can’t read the page, but they can usually see which website you’re visiting.
How the words fit together
An IP address says where the website lives. DNS finds that address from the name. HTTP is the conversation that fetches the page. HTTPS seals it.
The padlock means the connection is private, not that the site is honest. Scam sites can have a padlock too. Always check the web address itself.
When you'll hear it
“Is the site on HTTPS?” Does it have the padlock, so everything between you and it is sealed?
““Not secure” in the address bar.” The site uses plain HTTP. Don't type passwords or card details there.
“We need an SSL certificate.” The site needs the official ID card that lets browsers set up the sealed connection. Many are free today.
“Does every page we run use HTTPS, including the old ones?”