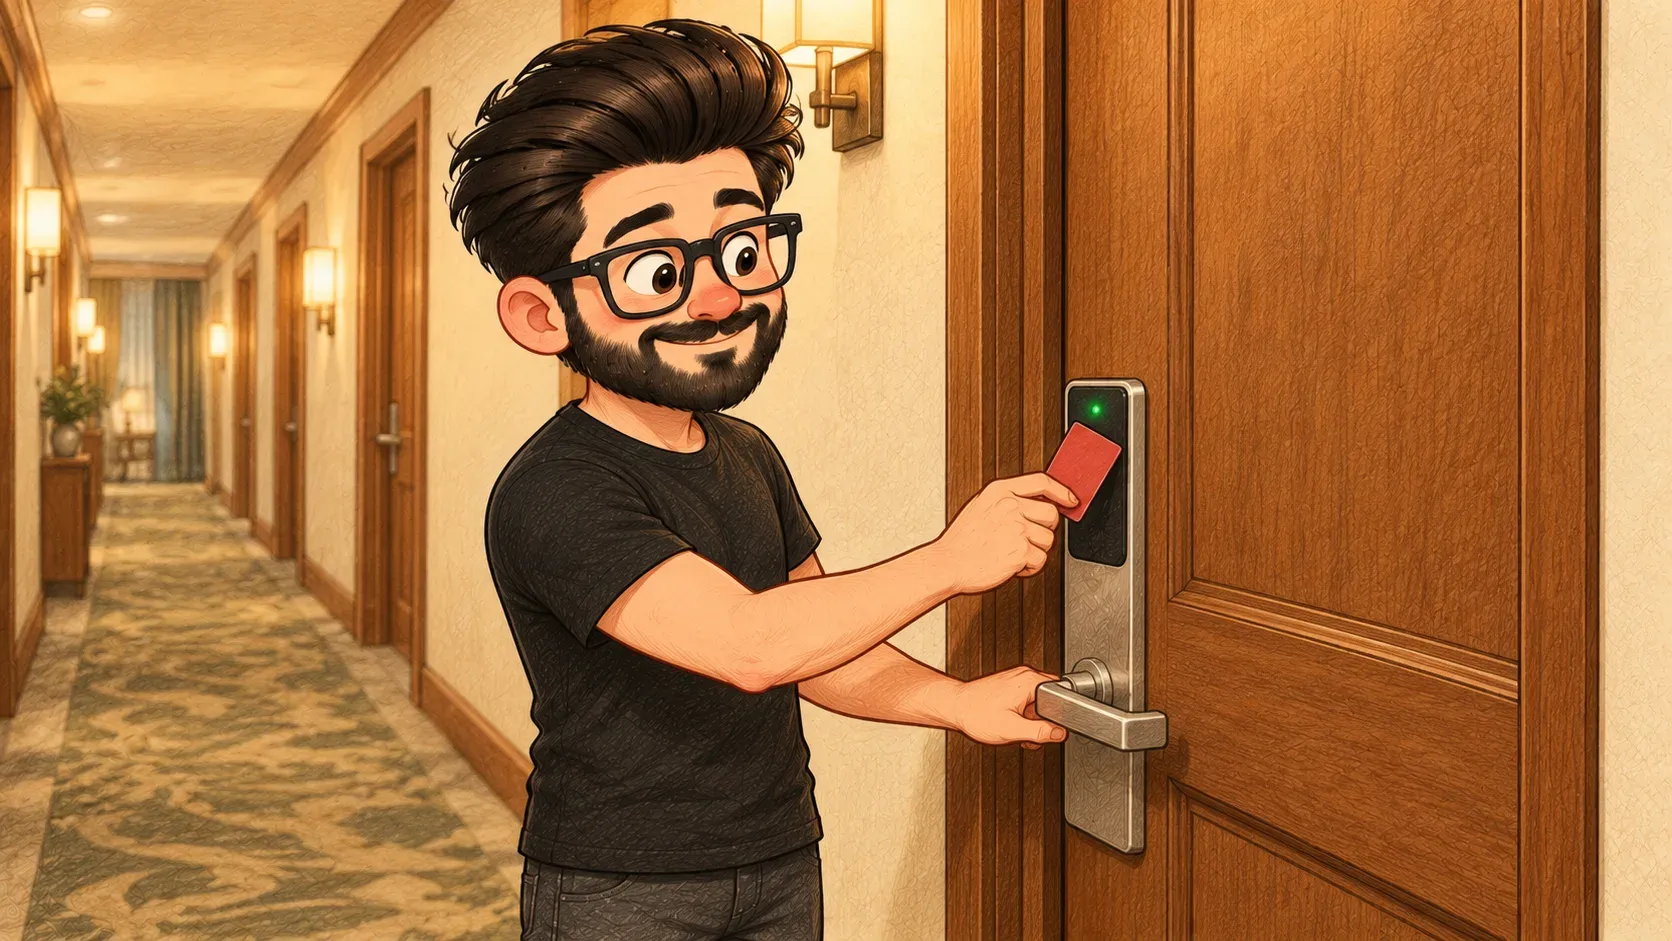

When your app knocks on another service's door, it needs to prove who it is. An API key is its key card.
At a hotel, your key card opens your room, maybe the gym, but not anyone else’s room. If you lose it, the desk cancels it and gives you a new one.
An API key works the same way for software. It’s a long secret code an app sends with every request, to prove which account it belongs to. The service then knows who’s asking, what they’re allowed to do and who to bill.
What it looks like
A long jumble of letters and numbers, often with a little label at the start, like sk-live-.... It’s meant to be impossible to guess.
Keeping it safe
- store it in a password manager or the app's secret settings
- never put it in shared documents, screenshots or public code
- give each app its own key, so you can cancel one without breaking the rest
What it isn’t
It isn’t your login password. It’s for software, not for a person signing in. Many services let you make lots of keys, each with different permissions.
Where the comparison breaks down
A stolen key card gets noticed quickly. A stolen API key can be quietly used for weeks, running up bills, until someone spots it.
How the words fit together
An API key unlocks an API. Its permissions decide which doors it opens. Keep it secret, like any password.
Treat an API key like a password. Never paste it into chats, emails or public code. If one leaks, cancel it and make a new one straight away.
When you'll hear it
“Don't commit the API key.” Don't save the secret into the project's shared code where others can see it.
“Rotate the key.” Swap the old secret for a new one, so the old one stops working.
“The key leaked.” Someone who shouldn't have it may now be able to use our account.
“Where are our API keys kept? Who gets told if one leaks?”

Try it yourselfReady to use it? The exact commands are on my other site, devcmds: Set an environment variable for good ↗
