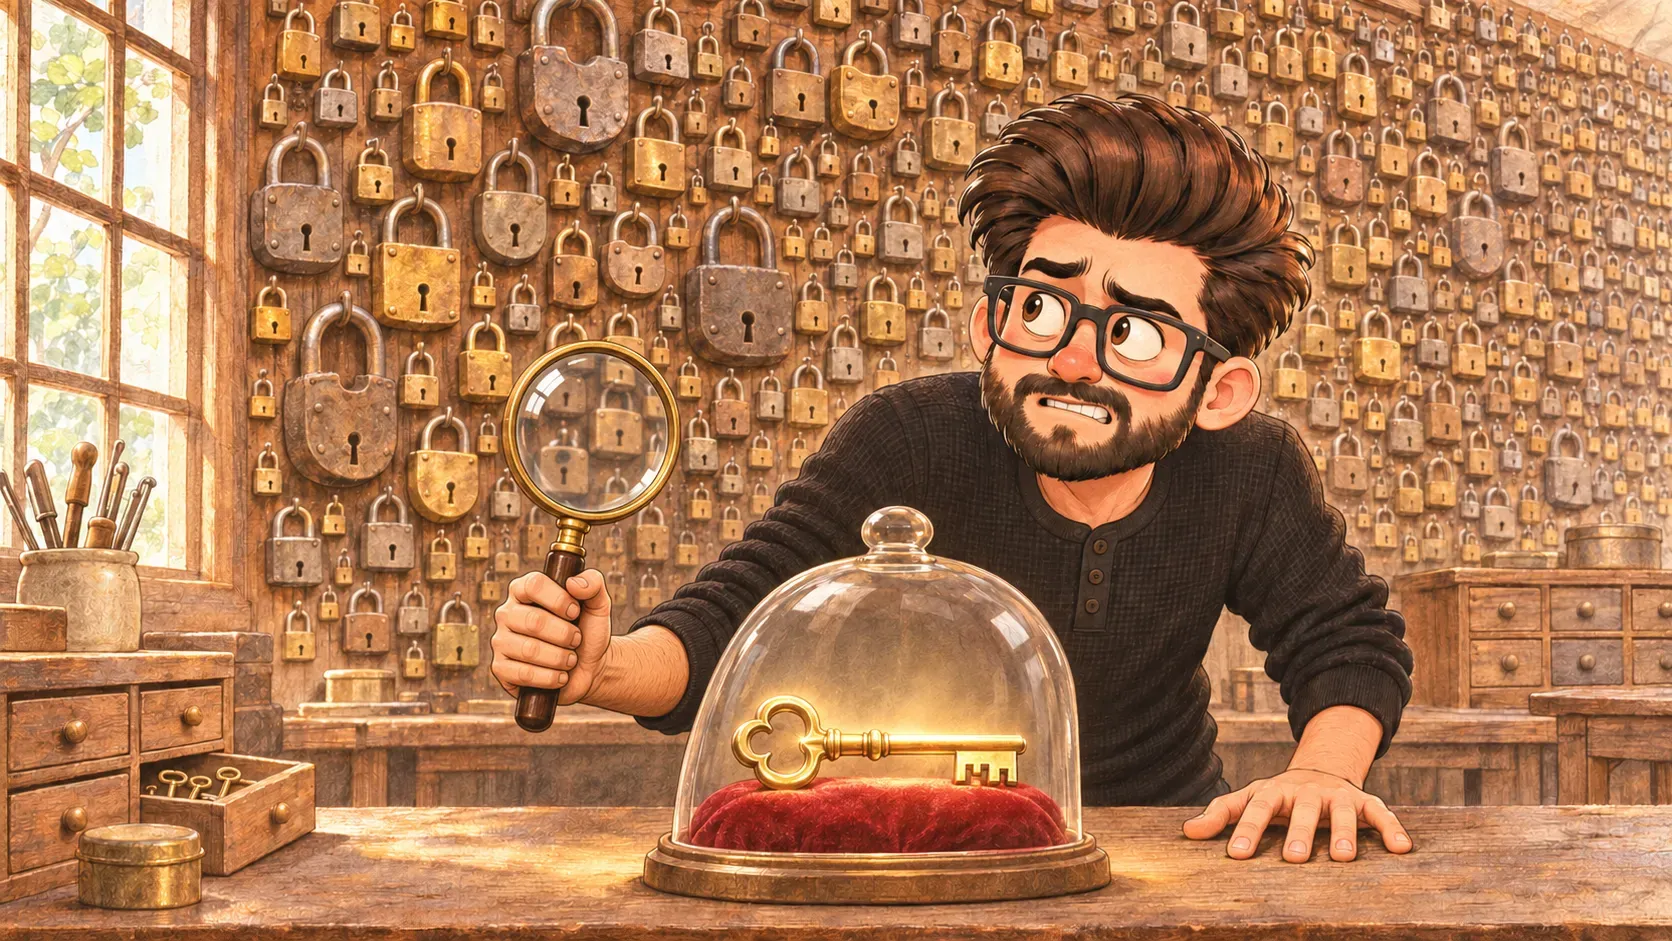

Most of the padlocks on the internet rely on one maths problem being far too slow to solve. Shor's algorithm makes it fast.
Picture a locksmith’s wall with thousands of padlocks. Each one is different, and picking any of them would take a lifetime. That’s why everyone trusts them. Now imagine someone describes how to make one master key that could open every padlock on the wall.
Shor’s algorithm is that description. It’s a method, written in 1994, that would let a big enough quantum computer break the encryption protecting most websites, messages and payments.
What it actually does
A lot of internet encryption relies on one fact: multiplying two huge numbers is easy, but working backwards to find them is so slow that no normal computer could do it in our lifetime. Shor’s algorithm lets a quantum computer do that backwards step quickly.
What it would break
- the padlock in your browser: how HTTPS agrees a secret with a website
- digital signatures: proof that an update or message is genuine
- many encrypted messages: if they were saved and kept
Why it hasn’t happened yet
Running it on real encryption needs a quantum computer with far more reliable qubits than anyone has built. Today’s machines are much too small and make too many mistakes. Nobody knows exactly when one will be big enough.
Where the comparison breaks down
A master key opens locks one at a time. Shor’s algorithm breaks the maths, so every lock built on that maths becomes weak at once. The fix isn’t a stronger padlock of the same kind: it’s post-quantum cryptography, a new kind of lock.
How the words fit together
Shor’s algorithm is the reason people worry about quantum computers and encryption. It’s why attackers might harvest now and decrypt later, and why the world is moving to post-quantum cryptography.
No quantum computer today is big enough to run it on real encryption. But secrets stolen now could be unlocked later, which is why the switch to new locks has already started.
When you'll hear it
“RSA isn't quantum-safe.” A big enough quantum computer running Shor's algorithm could break it.
“How many qubits would it need?” Far more good, error-free qubits than any machine has today.
“That's why we're moving to post-quantum.” We're changing to new locks that Shor's algorithm can't open.
“Which of our secrets would still matter in ten years if someone saved them today?”
