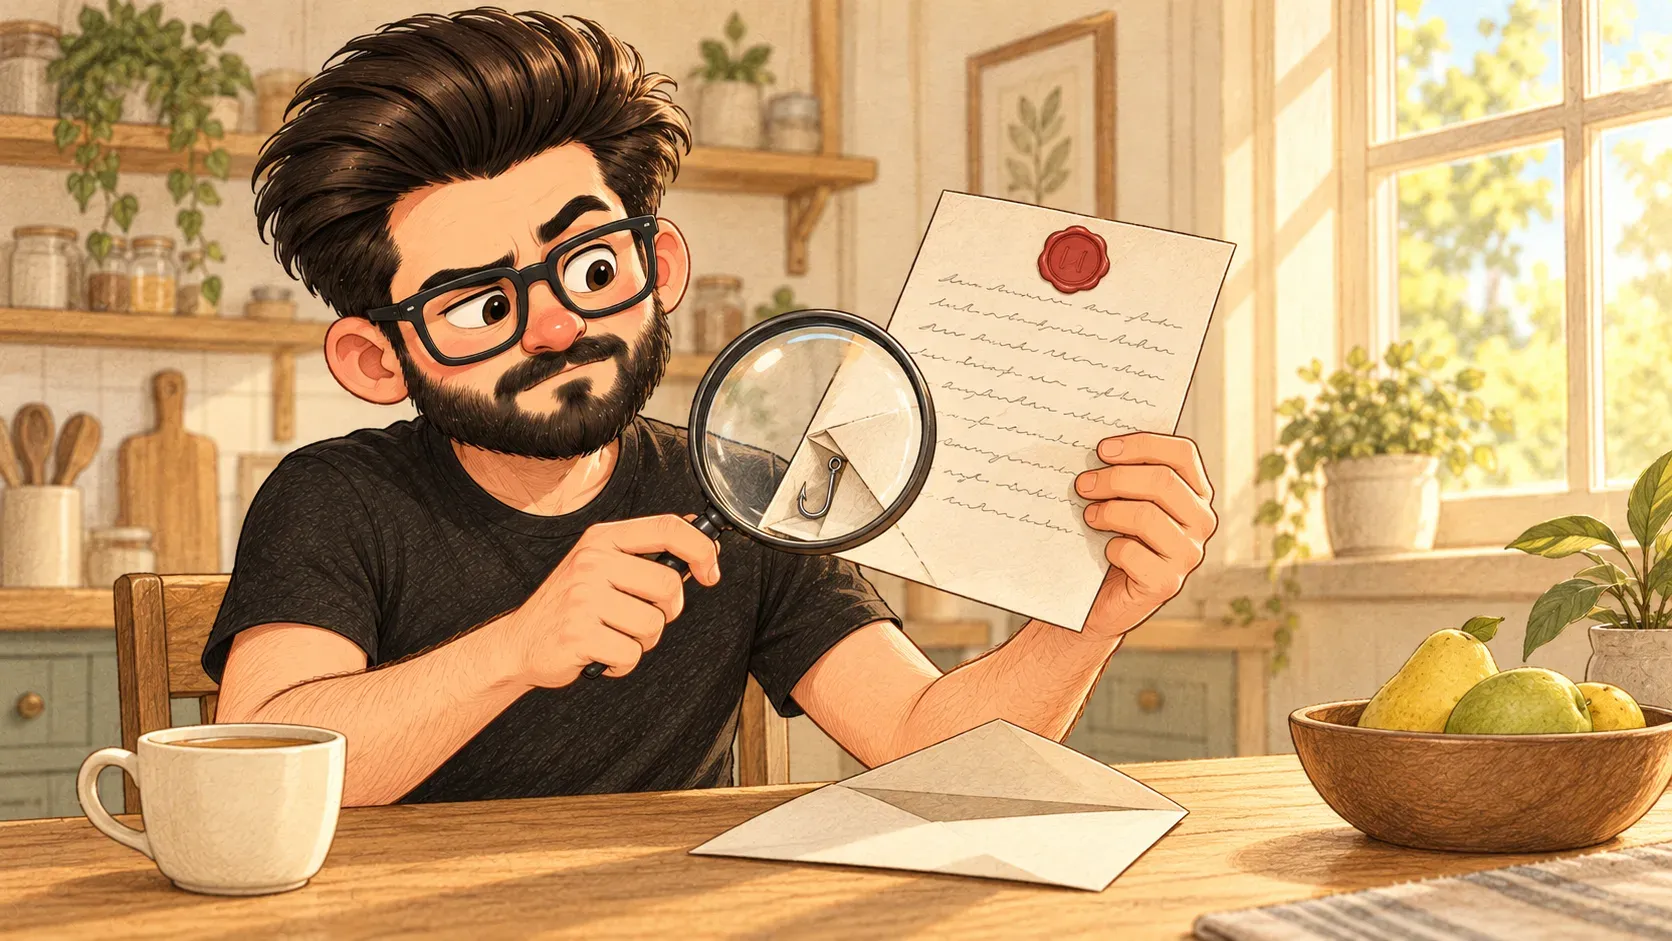

It looks like your bank. It sounds urgent. It asks you to click a link and sign in. That's phishing.
A letter arrives with your bank’s logo. “Unusual activity on your account. Reply today with your card number and PIN or your account will be closed.” It looks real. Your bank would never ask for your PIN.
That’s phishing. A message pretends to be from someone you trust, so you’ll hand over passwords, card details or money. The name comes from fishing: they cast out bait and wait for someone to bite.
Signs to look for
- a rush: “act now”, “last warning”, “your account will be closed”
- a link to a web address that's almost right, like paypa1.com
- a request for a password, a code or a payment
- a greeting like “Dear customer” instead of your name
Not just email
It also comes by text message, phone call, social media and even QR codes stuck on posters. The trick is the same everywhere: pretend to be trusted, then rush you.
What it isn’t
It isn’t a computer virus on its own. Phishing tricks the person. Sometimes the link also downloads malware, but the main aim is to fool you into helping.
Where the comparison breaks down
A fake letter takes effort to post. A phishing email costs almost nothing, so criminals send millions. Even if a tiny number of people bite, it pays.
How the words fit together
Phishing tries to steal your password. A password manager won’t fill it in on a fake site. Two-factor authentication stops a stolen password from being enough.
If a message rushes you, scares you or offers something too good, stop. Open the app or website yourself instead of clicking the link.
When you'll hear it
“That's a phishing email.” It's a fake message trying to trick you. Don't click anything in it.
“Report it as phishing.” Use the report button so the email team can block it for everyone.
“We're running a phishing test.” The company is sending pretend fake emails to see who clicks, so people learn to spot them.
“How do people here report a suspicious email? How quickly does someone look at it?”
