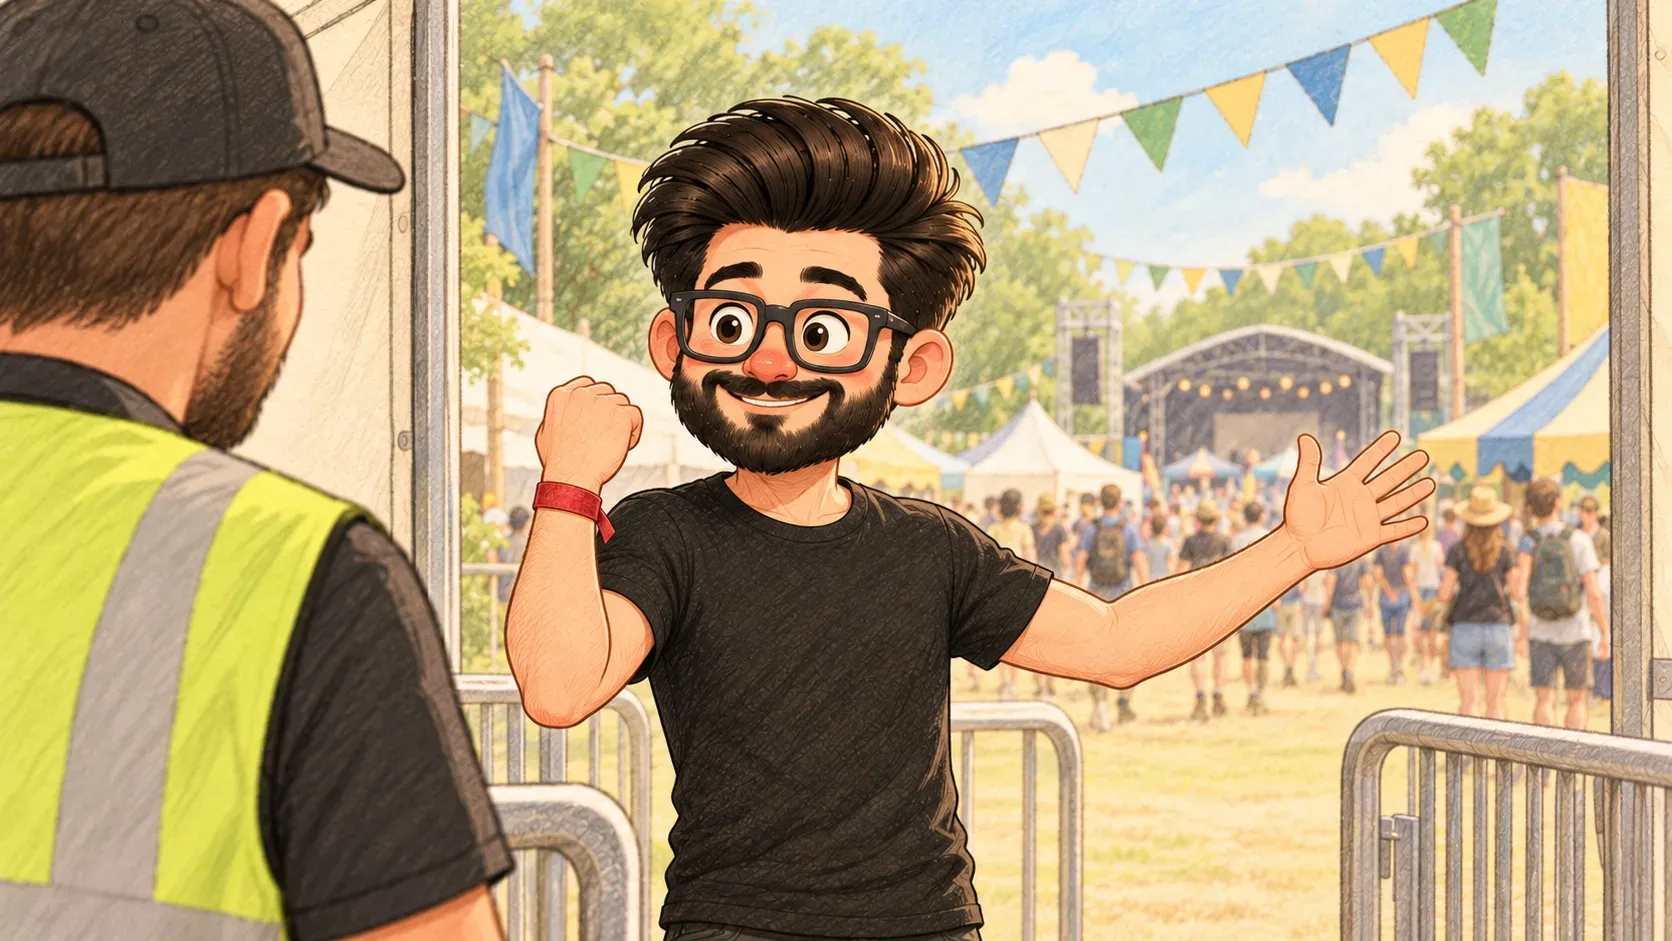
You sign in once and click around freely. The site hasn't forgotten you between pages. That's your session.
At a festival, you show your ticket once at the gate. You get a wristband. After that, you walk between stages freely: nobody checks your ticket again. The wristband is only good until the festival ends.
A session is that wristband. After you sign in, the website gives your browser a token that says “this person is signed in”. Every page you open shows it, so you aren’t asked to log in again.
How it ends
- you sign out
- you're away long enough that it times out
- you change your password, which often ends all sessions
Why it matters for safety
Whoever holds the wristband gets in. If someone copies your session, they can act as you without knowing your password. That’s why banks end sessions after a few minutes of quiet.
What it isn’t
It isn’t your password. The site checks your password once, then relies on the session.
Where the comparison breaks down
A festival wristband is the same for everyone. Each session token is unique and is usually kept inside a cookie in your browser.
How the words fit together
You sign in, maybe with 2FA. The site starts a session and stores its token in a cookie. Signing out ends it.
On a shared or public computer, always sign out when you're done. Closing the window doesn't always end your session.

When you'll hear it
“Your session has expired.” You were away too long, so the site forgot you and you need to sign in again.
“Sign out of all sessions.” Log yourself out on every device where you're still signed in.
“Someone stole a session.” An attacker copied the sign-in proof, so they could act as that person without a password.
“How long should people stay signed in to our tools before they're asked again?”
