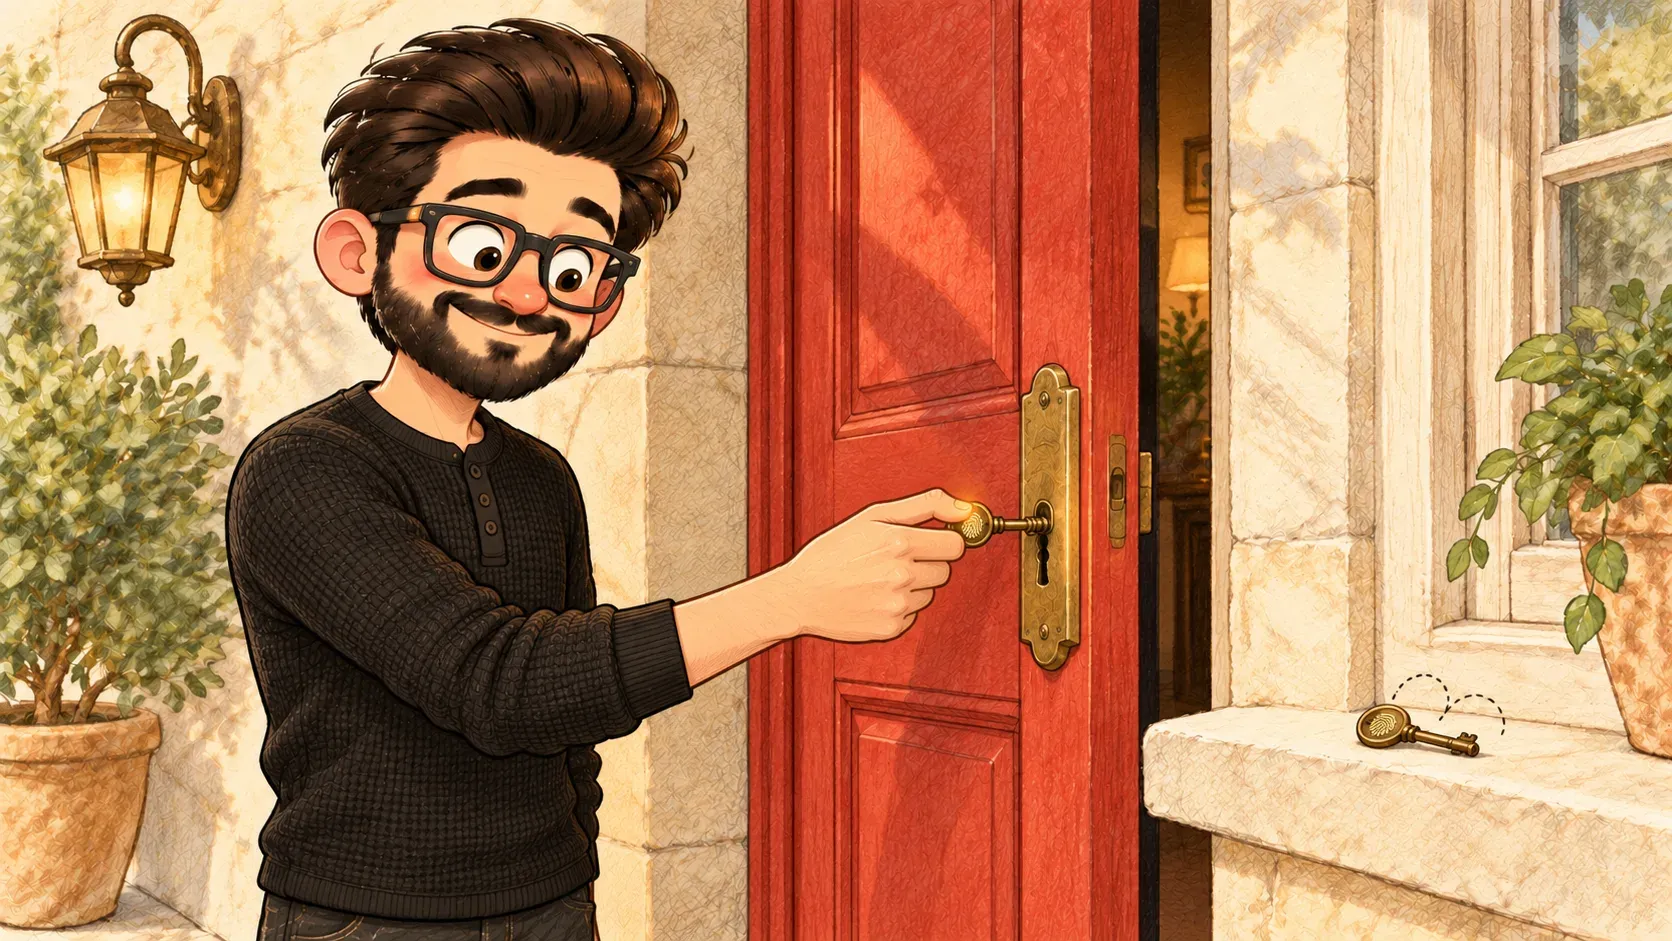

A password is a key anyone can copy if they see it. A passkey is a key that only turns when you're the one holding it.
A normal key works for anyone who holds it. Lose it or let someone copy it and they can walk right in. Passwords are the same: anyone who learns yours can use it.
Now imagine a key that only turns when it’s in your hand. Someone else could pick it up and it would do nothing. That’s a passkey: a way to sign in using your fingerprint, face or phone PIN instead of a password.
How it works
- when you set one up, your device makes a matching pair of secret keys
- one half stays locked on your phone or computer and never leaves it
- the other half is given to the website
- to sign in, you unlock your device with your finger, face or PIN and the two halves check each other
Why it’s safer than a password
- there's nothing to guess, forget or reuse
- a fake website can't use it, because it only works on the site it was made for
- if a website is hacked, the thieves only get the half that's useless on its own
What it isn’t
A passkey doesn’t send your fingerprint or face to the website. Your finger or face only unlocks your own device. The website never sees it.
Where the comparison breaks down
A real key is one object. A passkey can be copied safely to your other devices through your phone’s account or your password manager, so losing one phone doesn’t lock you out.
How the words fit together
A passkey replaces the password. It also does the job of two-factor authentication by itself, because you need both your device and your finger, face or PIN. It’s built to stop phishing and it uses encryption to keep the secret half safe.
When a site offers to create a passkey, say yes. Keep your password manager or phone backed up, so your passkeys come with you to a new device.
When you'll hear it
“Sign in with a passkey.” Use your fingerprint, face or phone PIN to log in, with no password to type.
“Passkeys can't be phished.” A fake website can't trick you into handing one over, because it only works on the real site.
“Your passkey is saved to your phone.” The secret part lives safely on your device and never gets sent to the website.
“Could our staff sign in with passkeys instead of passwords, so fake login pages stop working on them?”
